
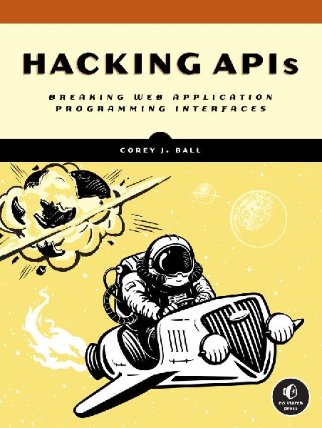
Hacking APIs
Autor: Susan M. Aposhyan

Nakladatel: Random House
Vazba: Brožovaná
EAN: 9781718502444
Typ produktu: Knihy
Pořadí vydání: 1.
Objednací číslo: 0716491
Hacking APIs is a crash course in web API security testing that will prepare you to penetration-test APIs, reap high rewards on bug bounty programs, and make your own APIs more secure.Hacking APIs is a crash course on web API security testing that will prepare you to penetration-test APIs, reap high rewards on bug...
Číst více Kniha

Doporučené tituly a kolekce

-122 Kč

-99 Kč
Default AIR carousel title
Více o produktu
POPIS
PODROBNOSTI
KATEGORIE
O AUTOROVI
Hacking APIs is a crash course in web API security testing that will prepare you to penetration-test APIs, reap high rewards on bug bounty programs, and make your own APIs more secure.
Hacking APIs is a crash course on web API security testing that will prepare you to penetration-test APIs, reap high rewards on bug bounty programs, and make your own APIs more secure.
You’ll learn how REST and GraphQL APIs work in the wild and set up a streamlined API testing lab with Burp Suite and Postman. Then you’ll master tools useful for reconnaissance, endpoint analysis, and fuzzing, such as Kiterunner and OWASP Amass. Next, you’ll learn to perform common attacks, like those targeting an API’s authentication mechanisms and the injection vulnerabilities commonly found in web applications. You’ll also learn techniques for bypassing protections against these attacks.
In the book’s nine guided labs, which target intentionally vulnerable APIs, you’ll practice:
- Enumerating APIs users and endpoints using fuzzing techniques- Using Postman to discover an excessive data exposure vulnerability- Performing a JSON Web Token attack against an API authentication process- Combining multiple API attack techniques to perform a NoSQL injection- Attacking a GraphQL API to uncover a broken object level authorization vulnerability
By the end of the book, you’ll be prepared to uncover those high-payout API bugs other hackers aren’t finding and improve the security of applications on the web.
Autor:
Nakladatel:
Typ produktu:
Knihy
Vazba:
Brožovaná
Pořadí vydání:
1.
Jazyk:
anglicky
Výška:
233 mm
Šířka:
176 mm
Hloubka:
23 mm
Hmotnost:
706 g
Počet stran:
368
Ean:
9781718502444
ISBN:
978-1-7185-0244-4
Vybíráme pro vás


-180 Kč

-178 Kč

-147 Kč

-275 Kč

-168 Kč

-182 Kč

-146 Kč
EN 1 460 Kč
1 314 Kč
1 248 Kč s PREMIUM

-170 Kč

-146 Kč

-144 Kč

-185 Kč
EN 1 849 Kč
1 664 Kč
1 581 Kč s PREMIUM

-248 Kč

-185 Kč

-165 Kč

-206 Kč

-167 Kč

-153 Kč
